
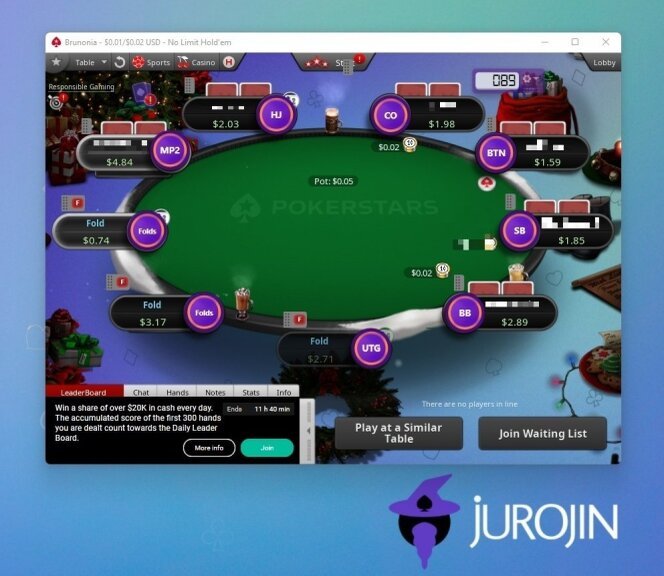
Around 30 high-stakes poker players may have been targeted through manipulated updates of third-party poker software. The attacker's apparent objective was to gain access to opponents' computers and potentially see their hole cards.
Details of a serious security incident affecting the online poker community have emerged in recent days. Rather than compromising poker room software directly, the attacker targeted third-party applications used by players.
One of the affected software providers, Jurojin, has now issued a detailed statement outlining the findings of its internal investigation.
According to the company, this was not a large-scale attack targeting its entire user base. Approximately 30 players, mostly playing at high stakes, may have been specifically targeted. Jurojin says all known affected users have been contacted directly.
Manipulated Updates Used to Gain Access
Jurojin is a third-party online poker tool offering features designed to assist with table management, hotkeys, bet sizing and multitabling.
Because the application runs alongside poker clients, compromising it can create a particularly serious security risk.
According to Jurojin's internal investigation, between June 2025 and June 2026, the attacker was intermittently able to deliver modified software packages to a specific group of users instead of the legitimate updates.
Some of these manipulated packages contained remote-access software. This could have allowed the attacker to see information displayed on a victim's computer — and in an online poker environment, that potentially includes the player's hole cards.
According to the company, the last known month in which the attack occurred was June 2026.
High-Stakes Players Were Specifically Targeted
Jurojin's investigation indicates that the operation was highly targeted.
The compromised software was not automatically distributed across a large portion of the user base. Instead, the attacker manually replaced update packages for a small group of selected players.
According to the statement, the same individual also targeted other applications used by online poker players. IntuitiveTables was among those affected, while the attacker allegedly also operated phishing websites impersonating poker rooms and well-known poker software.
Jurojin said a known cheater was believed to be behind the operation, primarily targeting high-stakes opponents in an attempt to monitor their computers and obtain information about their hole cards.
The method represents a different security threat from the classic "superuser" scandals previously seen in online poker, where access to a poker platform's internal systems made it possible to see opponents' cards.
In this case, the poker room itself did not need to be compromised. Instead, software running on the player's own computer became the potential entry point.
Jurojin Says It Reconstructed the Attack
Jurojin says it was able to retrospectively identify all relevant software versions distributed during the period under investigation.
The company was able to determine which versions had been manipulated and when those versions were delivered to affected players.
Jurojin says it will make the relevant data and logs available to law enforcement and cybersecurity specialists. The company is also cooperating with the cybersecurity researcher known as "Wolf," who brought the broader series of attacks targeting the online poker community to public attention.
According to Jurojin, some security measures already in place had made the attack more difficult even before the company became aware of the breach.
Among other measures, encryption keys used for communication between the application and its servers were regularly rotated. Jurojin believes this was one reason the attacker was only able to manipulate the system intermittently.
Additional Security Measures Introduced
Following the discovery of the compromised updates, Jurojin implemented additional security measures.
Access to sensitive configuration data has been tightened, all downloads from its servers are now logged, and multi-factor authentication has been introduced at points where critical server data can be modified or deleted.
Jurojin apologized to its users in its statement and said the lessons learned from the incident would be incorporated into its security systems going forward.
The case also highlights a broader security issue for online poker.
Player security does not depend solely on the protection offered by poker operators themselves. Any third-party application running alongside a poker client can potentially create another attack surface — and for high-stakes players, access to a computer screen could provide an attacker with one of the most valuable pieces of information possible: their opponents' hole cards.

0 comments